Services — 04
Cyber Security
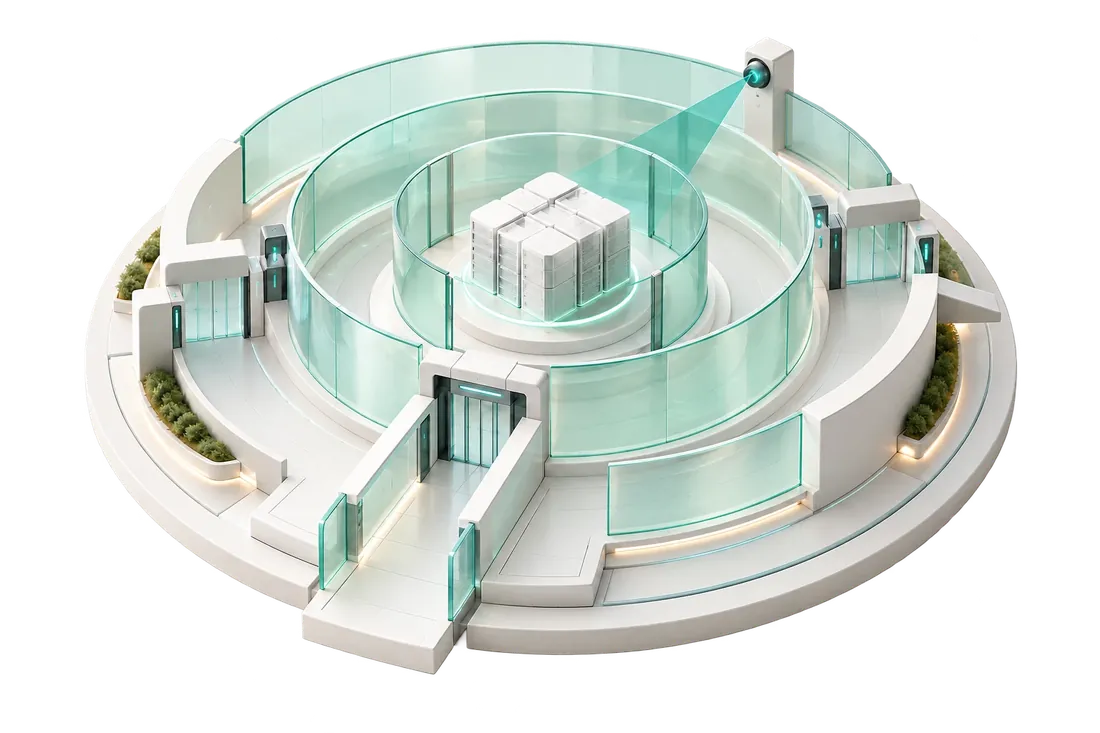
Security posture designed into the operating system from day one — not audited in after launch.
Offerings
What we deliver
- Security assessment & penetration testing
- Cloud security posture (AWS/Azure)
- Compliance readiness — SOC 2, ISO 27001, GDPR, PIPEDA / Quebec Law 25
- Secure SDLC & DevSecOps
Proof
Delivered with certified partners where the depth requires it; operated daily on the platforms we run.
Engagement models
- Fixed-scope build — Priced after discovery, milestone-billed.
- Operate — Monthly platform operation, support and improvements — the model Sceniq and UltimateDZM customers are on.
- Dedicated team — Resource deployment, month-to-month, 30-day notice.
- Studio partnership — Co-build and co-invest for a share of the venture.
In practice
A security engagement, end to end
Step 1
Scope — rules of engagement, systems in scope, constraints
Step 2
Assess — testing, posture review, threat surface
Step 3
Report — severity-ranked findings, written for owners and engineers
Step 4
Remediate — fixes delivered with your team or ours
Step 5
Re-test — verification that findings are closed
The process
Six stages, one named lead, a demo every two weeks.
01
Capacity call
Same week
02
Discovery
1–2 weeks
03
Architecture
1 week
04
Build
6–16 weeks
05
Launch & operate
Ongoing
06
Expand
Quarterly
Next step
Build like a giant. Move like a startup.
Book a 30-minute capacity call. We map where your business depends on people's hours — and what breaks that limit.